The cybersecurity world is currently reeling from one of the most significant threats to web infrastructure in years: the php2shell vulnerabilities (tracked as CVE-2026-109618 and CVE-2026-109619). Affecting almost every PHP version released in the last decade (versions 5.4 through 8.5), this critical flaw allows attackers to execute arbitrary code on vulnerable servers, completely compromising the website.
Because PHP powers nearly 80% of the web, including major CMS platforms like WordPress, Joomla, Drupal, and Magento, the attack surface is massive. While hosting providers and server admins are scrambling to update their systems, patching production servers takes time.
Fortunately, you don’t have to wait. Here is how the MoeSec Website Security Platform & Firewall acts as your ultimate shield against the php2shell exploit.
Why php2shell is Uniquely Dangerous
Unlike standard vulnerabilities that target poorly written plugins or themes, php2shell attacks the core PHP engine itself. Attackers exploit out-of-memory errors and memory corruption to achieve Remote Code Execution (RCE). This means a hacker can take full control of your web server, steal sensitive customer data, install ransomware, or deface your site.
Worse yet, because the vulnerability sits at the server’s core, standard WordPress or CMS security plugins often cannot stop it. If a plugin is bypassed or the hacker gains hosting access, those on-site security tools are instantly rendered useless.
How MoeSec’s Website Firewall Stops php2shell in Its Tracks
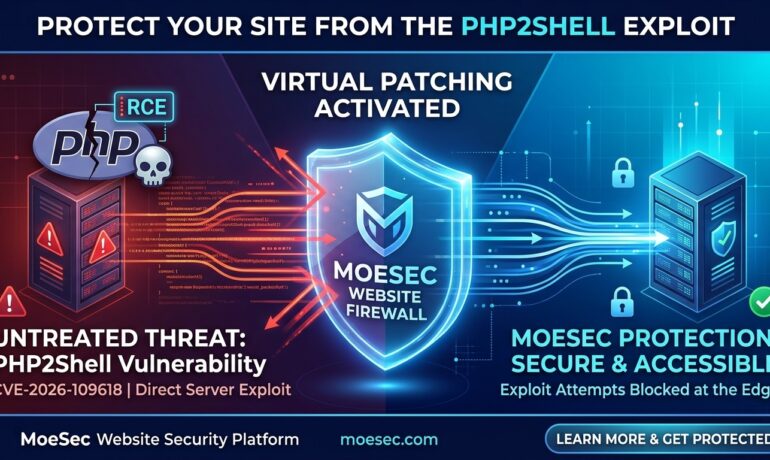
To protect against core-level threats like php2shell, you need edge-level security. The MoeSec Web Application Firewall (WAF) sits directly between your visitors and your website, filtering out malicious traffic before it ever touches your vulnerable server.
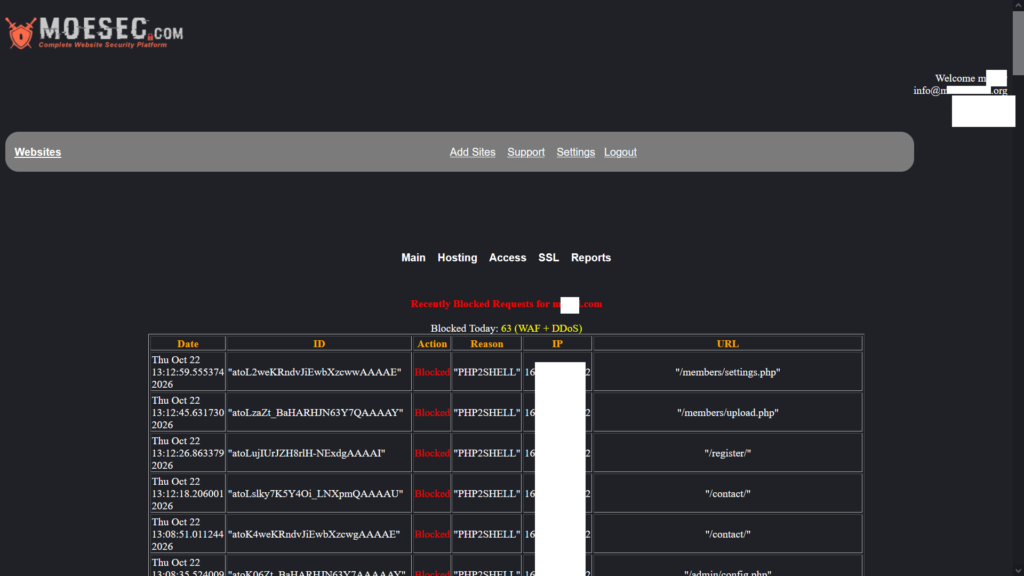
Here is how our platform neutralizes the threat:
1. Instant Virtual Patching You don’t have to wait for your hosting provider to update PHP. MoeSec’s firewall features Virtual Patching capabilities. As soon as zero-day threats and vulnerabilities like CVE-2026-109618 and CVE-2026-109619 are disclosed, our security experts implement network-level rules to detect and block the specific payloads attackers use to exploit the flaw.
2. Real-Time Traffic Filtering & Deep Packet Inspection Our WAF thoroughly inspects all incoming requests. By analyzing the traffic in real-time, MoeSec detects the malformed requests, abnormal memory-limit triggers, and malicious injections associated with php2shell, dropping the connection before the exploit reaches your PHP backend.
3. Isolated, Un-Bypassable Security Layer Because the MoeSec Firewall operates externally via DNS (simply pointing your A records to our secure IPs), it provides an isolated layer of defense. It cannot be disabled by corrupt updates, plugin conflicts, or even if an attacker attempts to tamper with your hosting account.
4. Comprehensive Coverage for Any Platform Whether you are running an outdated custom-coded site, or a heavily modified e-commerce store on Magento, Prestashop, or WordPress, MoeSec supports it all. The protection is platform-agnostic, keeping your business safe regardless of your CMS.
Don’t Wait for a Breach! Secure Your Site Today
Dealing with the aftermath of a data breach, lost trust, regulatory fines, and shattered reputation is exponentially more expensive than proactive protection.
Implementation takes just a few minutes with zero software to install. Protect your business from php2shell and future zero-day exploits today.